Loading
Topic
Access tokens
7 posts about Access tokens by 7 contributors.
Know Access tokens? Share what you know with developers who are learning it.
+ Follow Access tokensBe the first to follow this
- Articles
- 7
- Contributors
- 7
Everything about Access tokens
- Article · Security
Implementing OAuth 2.0 and OpenID Connect in ASP.NET Core
Learn how to implement OAuth 2.0 and OpenID Connect in ASP.NET Core. Secure applications with authentication, authorization, tokens, and Single Sign-On.
- Article · Web API
What Is OAuth 2.0 and How Does It Work in API Authentication?
OAuth 2.0 secures APIs by using tokens instead of passwords, granting limited access to user data. Learn how it works, its components, and benefits for apps.
- Article · Sharp Economy
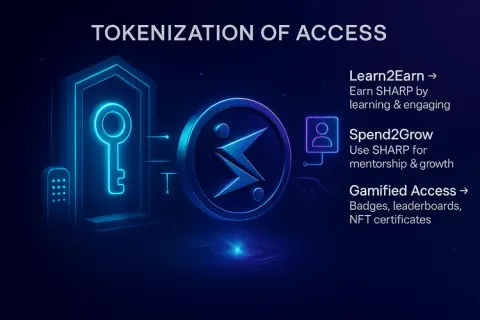
The Tokenization of Everything: How Web3 Is Turning Access Into Assets
Web3 tokenization is revolutionizing access, transforming intangible perks into tradable assets. Explore how projects like Sharp Economy are pioneering Learn2Earn and Spend2Grow models, empowering users to own and monetize their engagement, learning, and professional growth.
- Article · Security
Understanding Single Sign-On with Gmail for Third-Party Sites
Single Sign-On (SSO) with Gmail allows users to access third-party sites using their Google credentials. Implemented via OAuth 2.0 and OpenID Connect, it simplifies the login process, enhances security, and improves user experience.
- Article · ASP.NET
Token Based Authentication using Web API 2, Owin, and Identity
Implement secure token-based authentication in Web API 2 using Owin and Identity framework. Generate JWT tokens for user authentication, manage access and refresh tokens, and enforce authorization policies with ease, ensuring robust security for your API endpoints.
- Article · Security
Understanding Workflow Of OAuth2.0 Authorization Grant Types
In this article, you will learn about the workflow Of OAuth 2.0 Authorization Grant Types and define the workflow for obtaining access tokens, crucial for securing API access.
- Article · .NET Core
Identity API Endpoints based Authentication and Authorization in .NET 8
The second step in adding token-based authentication to ASP.NET Core Identity is to introduce the Identity API endpoints. Basically, this is an API version of the actions that you can perform with ASP.NET Core Identity through the classic web UI. Once you enable the Identity API endpoints, you will get endpoints like /register, /login, /forgotPassword, confirmEmail, etc.