Loading
Topic
MCP Security
10 posts about MCP Security by 7 contributors.
Know MCP Security? Share what you know with developers who are learning it.
+ Follow MCP SecurityBe the first to follow this
- Articles
- 10
- Contributors
- 7
Articles about MCP Security
- Article · AI Agents
MCP Servers in C#: How They Work and How to Build One
Learn how MCP servers expose tools to Claude, Copilot and ChatGPT, what the stateless 2026-07-28 spec changed, and how to build, connect and secure one in C#.
- Article · AI Agents
AI Agent Security: Where Controls Belong in the Stack
Learn where security belongs in an AI agent stack, from models and harnesses to runtime controls, credentials, tool access, audit logs, and recovery.
- Article · Cyber Security
GitHub Copilot MCP Allowlists: Securing AI Agent Tools in Enterprise Teams
Learn how GitHub Copilot MCP allowlists can secure AI agent tools in enterprise environments by controlling tool access, permissions, trusted servers, and agent capabilities.
- Article · AI Agents
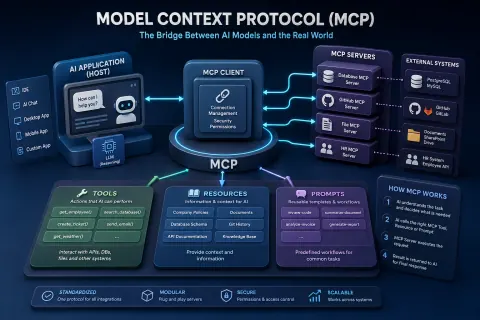
Model Context Protocol (MCP): The Bridge Between AI Models and the Real World
Learn what Model Context Protocol (MCP) is, how hosts, clients, servers, tools, resources, and prompts work, and how MCP connects AI agents with enterprise systems.
- Article · AI
Securing MCP Servers Against Prompt Injection and Tool Poisoning
Secure MCP servers against prompt injection & tool poisoning. Learn AI-specific risks & implement practical production security measures.
- Article · ASP.NET Core
MCP Security Best Practices: Authentication, Authorization, and Secure Tooling
Secure your .NET MCP implementations with best practices for authentication, authorization, and tool design to protect AI integrations and enterprise data.
- Article · AI
How MCP Apps Are Changing AI Tool Integration Workflows
Learn how MCP Apps are transforming AI tool integration workflows by providing standardized access to APIs, databases, business systems, and enterprise resources through the Model Context Protocol.
- Article · C#
How to Build Custom MCP Servers in C# for Enterprise AI Applications
Learn how to build custom MCP servers in C# for enterprise AI applications. Discover MCP architecture, security best practices, tool development, authentication, and real-world integration patterns.
- Article · AI
Model Context Protocol (MCP) Security: Preventing Prompt Injection and Tool Hijacking
Learn how to secure Model Context Protocol (MCP) applications by preventing prompt injection, tool hijacking, unauthorized access, and other AI security threats using proven enterprise security practices.
- Article · AI Agents
AI Agent Security Risks Every Developer Should Understand
Learn the most important AI agent security risks including prompt injection, data leakage, excessive permissions, and secure AI development best practices.