Loading
Topic
OllyDbg
2 posts about OllyDbg by 2 contributors.
Know OllyDbg? Share what you know with developers who are learning it.
+ Follow OllyDbgBe the first to follow this
- Articles
- 2
- Contributors
- 2
Everything about OllyDbg
- Article · .NET
Applied Reverse Engineering With OllyDbg
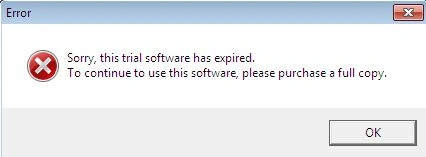
This paper explores executable cracking using OllyDbg, focusing on reverse engineering without source code. It emphasizes Assembly Programming and tools like OllyDbg and CFF Explorer. Methods include patching binaries to bypass copy protection. A trial software example demonstrates debugging and modifying code to remove expiration.
- Article · Networking
How To Reverse Engineer Using OllyDbg
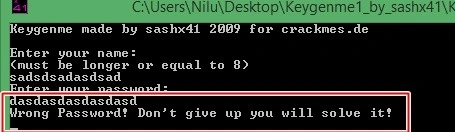
This article provides an introduction to obfuscation and reverse engineering, focusing on using OllyDbg as a reverse engineering tool. It explains the concept of obfuscation as a means to secure source code from reverse engineering attempts. The article demonstrates how to reverse engineer an EXE file, using a keygen.exe example to illustrate the process.