Red Team
2 posts1 contributor
+ FollowBe the first to follow this
Write about itArticles about Red Team
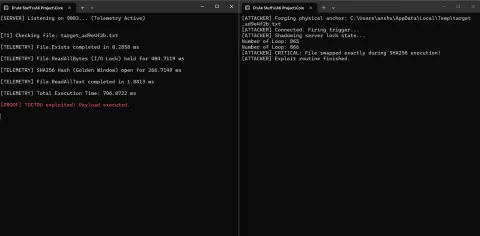
Anatomy of a .NET Race Condition: Exploiting and Patching TOCTOU Vulnerabilities (Phase 04 of 16)
Master .NET application security. Learn how attackers weaponize TOCTOU file system race conditions (CWE-367) and how senior architects patch them using deterministic memory snapshots and the Acquire-Check-Use pattern.

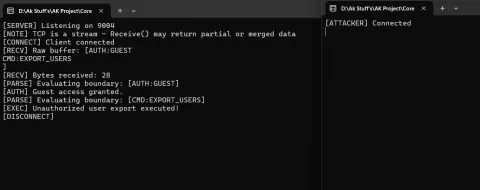
Offensive Socket Security in .NET: Weaponizing C# Parsers - State Desynchronization over TCP (Phase 05A)
A critical mistake in .NET network programming is treating a continuous TCP stream like a discrete message queue. Discover how Parser State Desynchronization can lead to authorization bypasses in custom protocols. This deep-dive explores the underlying mechanics of socket state management, provides a C# proof-of-concept, maps to real-world CWEs, and outlines the exact architectural patterns needed to secure enterprise systems.