Loading
Topic
secure AI
6 posts about secure AI by 4 contributors.
Know secure AI? Share what you know with developers who are learning it.
+ Follow secure AIBe the first to follow this
- Articles
- 6
- Contributors
- 4
Everything about secure AI
- Article · AI Agents
MCP Servers in Practice: Building Secure Tool Integrations for AI Agents
Discover MCP Servers for secure AI agent tool integrations. Standardize, simplify, and enhance security for dynamic external system access.
- Article · AI Agents
How to Prevent Prompt Injection Attacks in AI Applications?
Protect AI apps from prompt injection! Learn to secure LLMs with strong prompts, input validation, output filtering, & AI guardrails. Build safer AI systems.
- Article · AI Agents
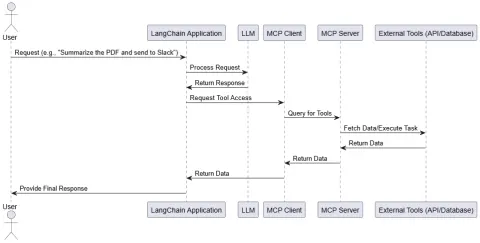
AI Agent–Tool Abstraction Architecture
Build robust AI apps with LangChain & MCP! LangChain orchestrates tasks, while MCP secures tool access. Modular, scalable, & secure AI architecture.
- Article · Cyber Security
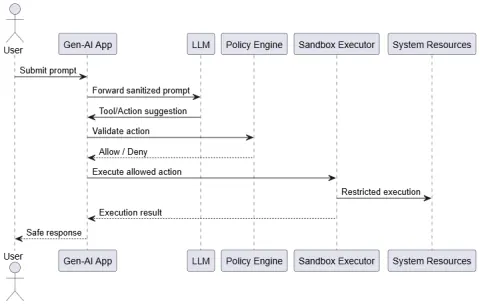
Fix RCE (Remote Code Execution) issue in Gen-AI
Secure Gen-AI by fixing Remote Code Execution (RCE) vulnerabilities! Learn how to protect your systems with sandboxing, policy enforcement, and secure architecture.
- Article · AI
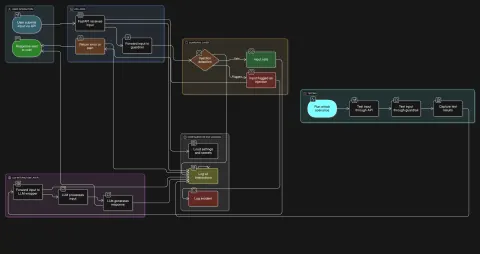
Case Study: Secure Legal Assistant — An Enterprise AI System That Refuses to Break Confidentiality, Even When Ordered To
Protect your AI applications from prompt injection attacks! This guide provides a technical deep dive, code examples (Python, FastAPI), and defense strategies to build a secure AI chat API. Learn to detect, block, and log malicious prompts, ensuring confidentiality and compliance in enterprise AI systems. Includes a legal assistant use case.