Loading
Topic
Secure SDLC
3 posts about Secure SDLC by 2 contributors.
Know Secure SDLC? Share what you know with developers who are learning it.
+ Follow Secure SDLCBe the first to follow this
- Articles
- 3
- Contributors
- 2
Everything about Secure SDLC
- Article · Angular
The Evolution of Web Security: Best Practices for 2025 and Beyond
Explore the evolution of web security and best practices for 2025 and beyond. Covers modern threats, secure development, API and frontend protection, and cloud security. Designed for senior developers building resilient and future-ready web applications.
- Article · Software Testing
Automated Threat Modeling: Integrating Security Design into Agile Development
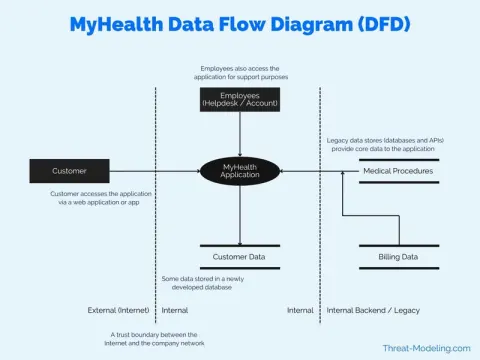
Threat modeling is a structured approach to identifying and mitigating potential security risks in a system. It involves analyzing the architecture, data flows, and components of an application to uncover vulnerabilities and design flaws before they can be exploited. The goal is to proactively address security concerns during the design and development phases.
- Article · Software Testing
Security Testing Automation: Integrating SAST and DAST in Pipelines
Security testing automation is essential in modern DevSecOps practices. Integrating Static Application Security Testing (SAST) and Dynamic Application Security Testing (DAST) into CI/CD pipelines ensures early detection and remediation of vulnerabilities.