security best practices
9 posts7 contributors
Articles about security best practices

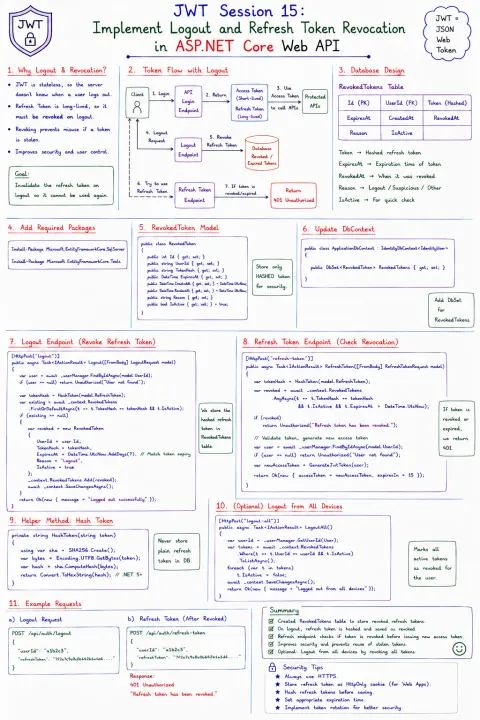
JWT Session 15: Implement Logout and Refresh Token Revocation in ASP.NET Core Web API
Secure your JWT-based ASP.NET Core API by implementing robust logout and refresh token revocation to prevent session hijacking and unauthorized access.

Azure Key Vault Best Practices
Master Azure Key Vault best practices for ASP.NET Core. Securely manage secrets, keys, and certificates, enhancing application security.
Azure Key Vault Best Practices for Managing Application Secrets
Master Azure Key Vault best practices for secure application secrets management, including Managed Identity, least privilege, and CI/CD integration.
How to Safely Rotate API Keys Without Breaking Applications
Learn how to rotate API keys safely and avoid application downtime. This guide covers key rotation strategies, secure storage, and monitoring best practices. Keep your systems secure!
How Can Teams Audit Data Access When Using Shared Service Accounts?
Learn how to audit data access from shared service accounts using detailed logging, contextual metadata, short-lived credentials, least privilege, and anomaly monitoring.
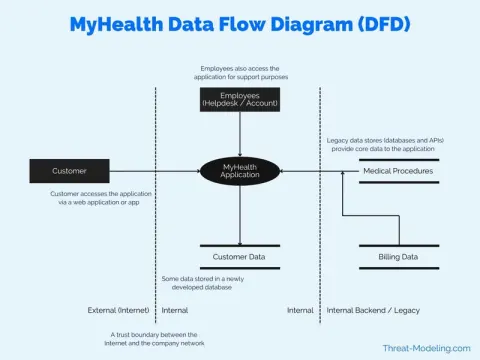
Automated Threat Modeling: Integrating Security Design into Agile Development
Threat modeling is a structured approach to identifying and mitigating potential security risks in a system. It involves analyzing the architecture, data flows, and components of an application to uncover vulnerabilities and design flaws before they can be exploited. The goal is to proactively address security concerns during the design and development phases.
Security Testing Automation: Integrating SAST and DAST in Pipelines
Security testing automation is essential in modern DevSecOps practices. Integrating Static Application Security Testing (SAST) and Dynamic Application Security Testing (DAST) into CI/CD pipelines ensures early detection and remediation of vulnerabilities.
Securing Your Workloads in VMware Cloud
Fortify your VMware Cloud environment! Discover essential security practices for access control, networking, disaster recovery & more. #VMwareCloud #CloudSecurity
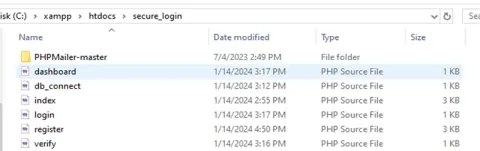
Building a Secure PHP MySQL Signup/Login Website with Email Verification
Build a PHP and MySQL signup/login system with password hashing, prepared statements, and Gmail email verification using PHPMailer.