Loading
Topic
SIEM
6 posts about SIEM by 4 contributors.
Know SIEM? Share what you know with developers who are learning it.
+ Follow SIEMBe the first to follow this
- Articles
- 6
- Contributors
- 4
Everything about SIEM
- Article · Cyber Security
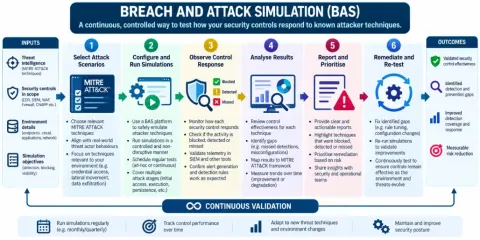
Breach and Attack Simulation vs. Security Control Validation vs. Agentic AI Penetration Testing
Compares breach and attack simulation, security control validation, and agentic AI penetration testing, explaining the questions each approach answers and how they complement one another.
- Article · SQL Server
What Strategies Help Monitor and Detect Suspicious Activity in Backend Systems?
Protect backend systems! Learn strategies for monitoring and detecting suspicious activity, from centralized logging to SIEM, ensuring data security and uptime.
- Article · Cyber Security
Implement SIEM in Enterprise Solutions
Enhance enterprise security with SIEM! This guide covers implementation, benefits, and how SIEM provides real-time threat detection, compliance, and incident response.
- Article · Microsoft Teams
Connect Entra ID Logs to Microsoft Sentinal
Secure your Microsoft environment by connecting Entra ID logs to Microsoft Sentinel. This integration provides real-time threat detection, automated incident response, and enriched investigations using KQL. Learn how to ingest Audit, Sign-in, Provisioning, and Risk Events, fulfilling prerequisites, and troubleshooting common issues to enhance your SecOps capabilities and protect against identity-based attacks. This setup is a must for modern SecOps.
- Article · Cyber Security
What is UEBA (User and Entity Behavior Analytics) in SIEM
UEBA (User and Entity Behavior Analytics) enhances SIEM by using AI to detect unusual behavior from users or devices, helping identify insider threats, anomalies, and advanced cyberattacks in real-time.
- Article · Cyber Security
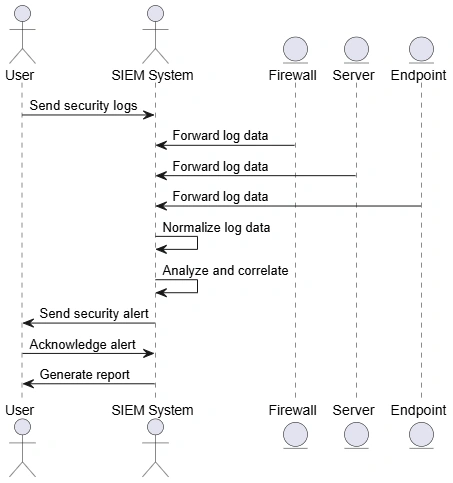
What Is SIEM
Learn about what is SIEM [ Security information and event management ] and its roles.