Loading
Topic
Microsoft Sentinel
3 posts about Microsoft Sentinel by 2 contributors.
Know Microsoft Sentinel? Share what you know with developers who are learning it.
+ Follow Microsoft SentinelBe the first to follow this
- Articles
- 3
- Contributors
- 2
Everything about Microsoft Sentinel
- Article · Microsoft Teams
Connect Entra ID Logs to Microsoft Sentinal
Secure your Microsoft environment by connecting Entra ID logs to Microsoft Sentinel. This integration provides real-time threat detection, automated incident response, and enriched investigations using KQL. Learn how to ingest Audit, Sign-in, Provisioning, and Risk Events, fulfilling prerequisites, and troubleshooting common issues to enhance your SecOps capabilities and protect against identity-based attacks. This setup is a must for modern SecOps.
- Article · Azure
Configuring Data Connector And Producing Activity Data in Microsoft Sentinel
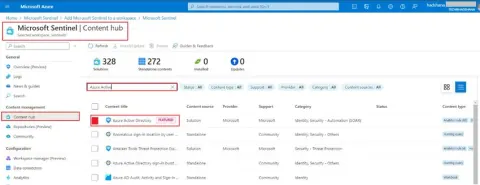
Configuring the data connector and producing activity data in Microsoft Sentinel. the configuration process of a data connector and the generation of activity data in Microsoft Sentinel. It demonstrates the installation of a data connector for Azure Activity through the Content Hub in Microsoft Sentinel. Users are guided through the installation/update process, verification of the installation success, and subsequent configuration of the data connector. The tutorial then proceeds to illustrate the creation of activity data by enabling a rule within the Azure Activity solution for Microsoft Sentinel.
- Article · Azure
How to Set Up Microsoft Sentinel?
How to Set Up Microsoft Sentinel. Set up Microsoft Sentinel with ease using this step-by-step guide. Learn to navigate the Azure portal, create a new workspace, and install necessary components, ensuring comprehensive threat intelligence and security analytics for your organization. Stay tuned for Series-02, which covers data connector configuration and activity data production in Microsoft Sentinel.